▸ Tag · #security
Security.
Security for systems that talk to models and to money: authentication, webhook verification, and denial-of-wallet on metered AI endpoints.
-
 Laravel
MCP auth and audit logging in a Laravel SaaS
An MCP server on Laravel is only as safe as its tenancy boundary. Scoped tool auth, request-bound actor context, and an audit log you can actually read at 3am.
Read post →
-
 Shopify
Building secure agentic commerce on Shopify in 2026
How agentic commerce on Shopify stays safe: UCP negotiation, an MCP governance layer, scoped credentials, signed requests, and human approval at checkout.
Read post →
-
 Laravel
Your Laravel MCP server now checks Origin. APP_URL just became a security setting.
Laravel MCP 1.2.0 returns 403 to a browser request whose Origin is not your APP_URL. That makes APP_URL part of your MCP security, and the allow list is a config key that is not in the config file.
Read post →
-
 DevOps
Write is not delete: Coolify just changed your API and MCP contract
Coolify 4.6 and 4.7 changed the contract: a write token can no longer delete, and a newer git push cancels the older queued webhook deploy by default.
Read post →
-
 AI
Meta Muse for Solo Founders: The Guard Outside the Agent Matters More Than the Agent
Meta's personal agent takes action on its own cloud computer and keeps working after you close the app. Sentinel sits outside the model. Price as of 28 October 2026.
Read post →
-
 AI
OpenAI Dots for Solo Founders: An Always-On Agent in Slack and Teams, on Your Rules
One always-on ChatGPT agent keeps working on its own cloud computer after you close the laptop. Custom Rules, Slack and Teams, and the Pro price as of 28 October 2026.
Read post →
-
 AI
Grok Bot for Solo Founders: Named AI Teammates on One Shared Computer
Named AI teammates share one cloud computer and keep working after you close the laptop. Parallel work, approvals, and The X Subscription price as of 27 October 2026.
Read post →
-
 AI
Claude Duet: a proactive agent that waits for your ok
Claude Duet briefs you in the morning and waits before send, pay, or delete. What Anthropic has published, and why a solo founder might join the US Pro and Max waitlist.
Read post →
-
 Laravel
Stop sending your Laravel search filters as POST
Laravel 13.35 adds Route::query(), so a search endpoint can take a JSON body and still say it is read only. Here is why I would move internal search endpoints to QUERY now, and the three things to check first.
Read post →
-
 DevOps
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35: update your Laravel servers today
PHP shipped fixes for two critical remote code execution bugs on 21 October 2026. Here is what is affected, what the interim settings do, and how to rebuild and redeploy a Laravel app in Docker.
Read post →
-
 AI · Updated Oct 29, 2026
Claude Duet vs Grok Bot vs OpenAI Dots vs Meta Muse: pick by control and access
Four personal agents each keep a cloud computer working after you close the laptop. Pick by who says yes before a send or a payment, and whether your plan and country can get in.
Read post →
-
 AI
Run your business with one AI assistant per area
A simple setup for running any business with AI assistants: one hub, one bot per area of work, strict scopes, drafts before sends, and routines that stay quiet.
Read post →
-
 Architecture
HITL gates for agent mutations
Human-in-the-loop risk gates for refunds, inventory, and spend. Verify mutations after tool calls so agents cannot declare early victory.
Read post →
-
 Laravel
MCP OAuth PKCE for multi-tenant SaaS
Laravel MCP requires PKCE S256 and prefers Client ID Metadata Documents. How multi-tenant SaaS should bind workspace at consent and avoid common agent auth failures.
Read post →
-
 Shopify
Buyer-linked tokens for agent checkout
Exchange a Shop session for a Shopify buyer-linked JWT (~60 minutes, no refresh) so signed-in agents can personalize catalog and complete checkout.
Read post →
-
 Shopify
UCP agent profiles are the new OAuth app
Host a UCP agent profile URL, declare cart and checkout capabilities, and climb Anonymous, Signed, and Token trust tiers for Shopify MCP.
Read post →
-
 Laravel
MCP tool errors agents can actually recover from
Throwing exceptions hides failures from the model. MCP wants isError tool results with actionable text, mapped from Laravel domain failures and audited like auth denials.
Read post →
-
 Laravel
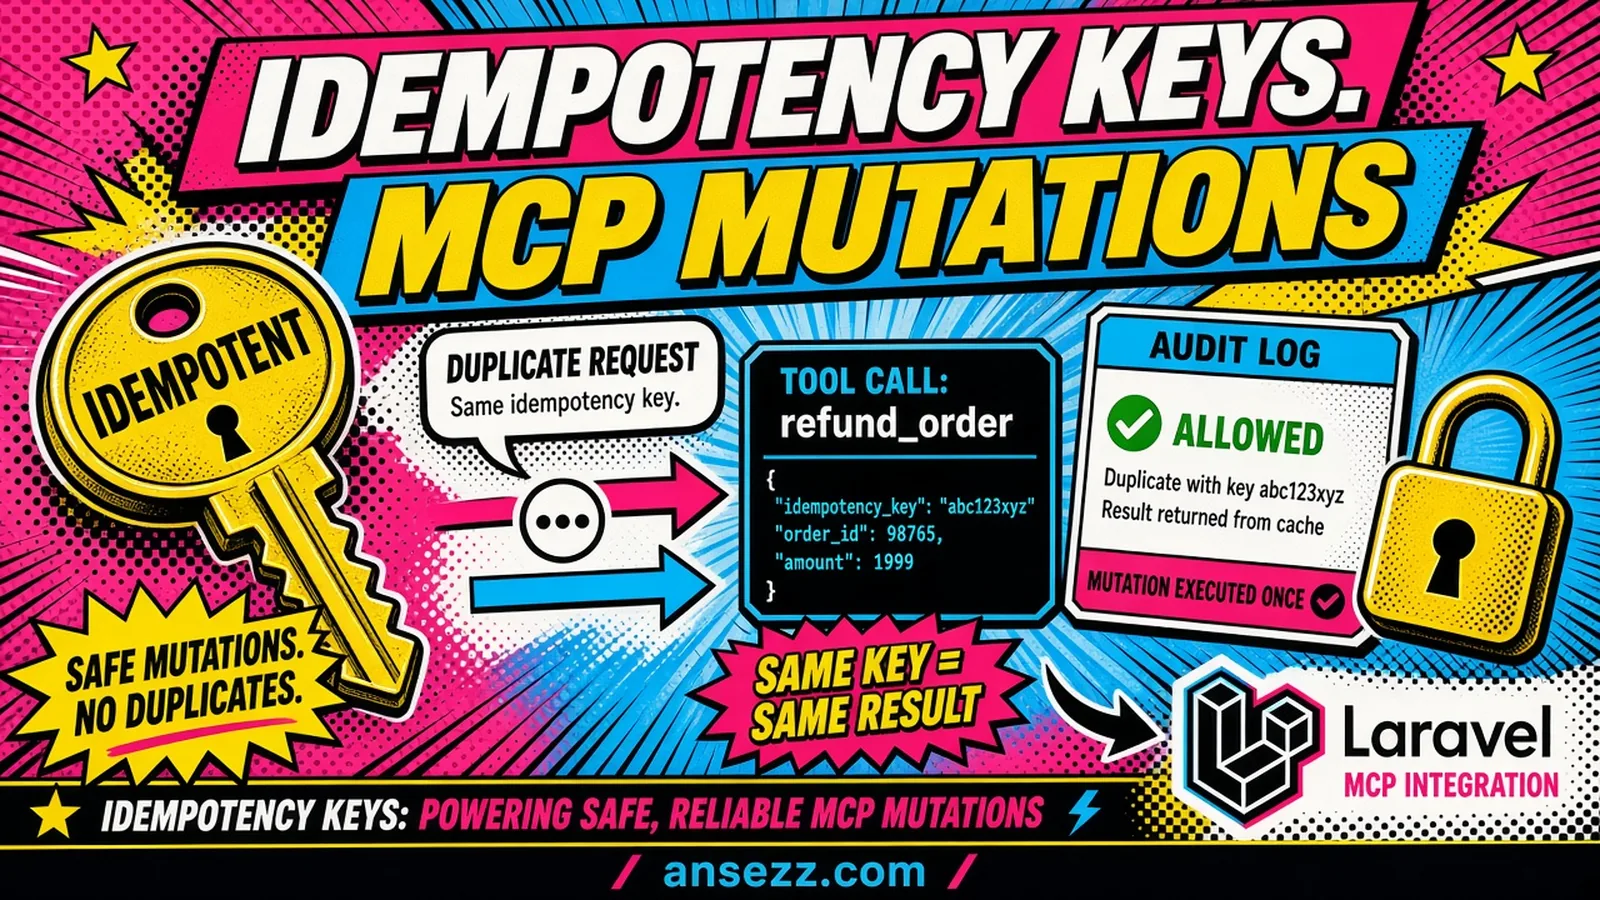
Idempotency keys for MCP mutations in Laravel
Refunds, seat resets, and password emails need more than audit logging. Client-supplied idempotency keys, server-side short-circuits, and race-safe storage under Octane.
Read post →
-
 DevOps
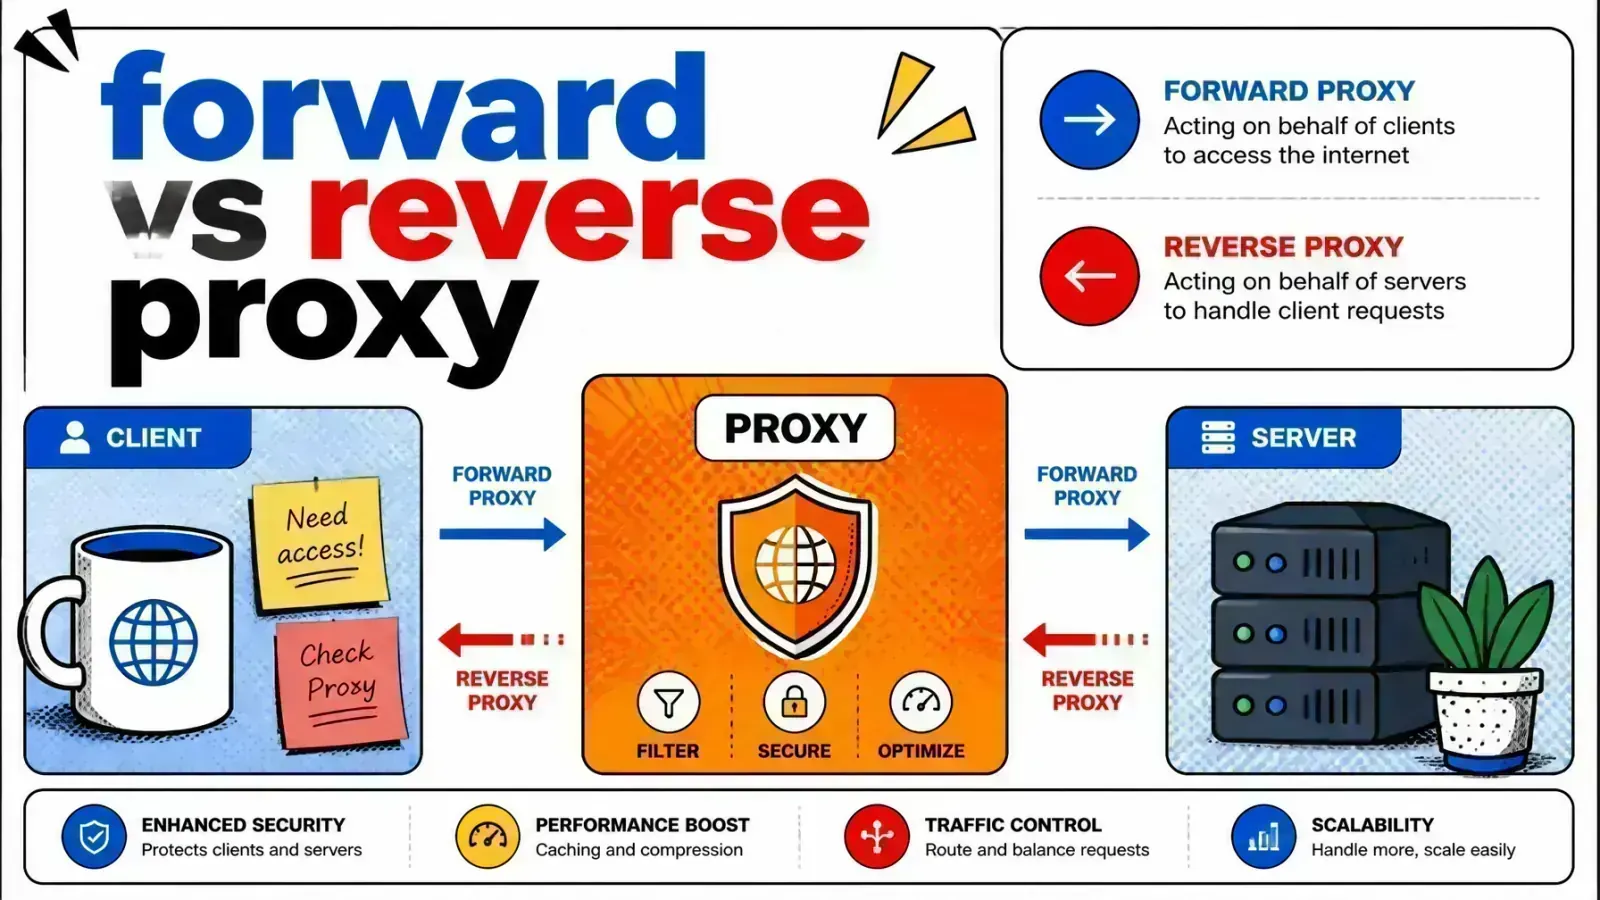
Forward proxy vs reverse proxy: the technical guide
A forward proxy hides the client; a reverse proxy hides the server. How traffic direction shapes your load balancing, SSL termination, and security design.
Read post →
-
 Architecture
Rate limiting: protecting your AI wallet
One runaway agent loop can mean a $5,000 LLM bill. Why request-per-second limits lie, and how hierarchical token-bucket limits protect your margins.
Read post →
-
 Architecture
API gateway: the front door of your AI stack
Stop exposing LLM providers to your frontend. The API gateway pattern for AI apps: tenant isolation, model aliases, rate limiting, and streaming-safe timeouts.
Read post →